Blind Eagle Uses Fake Court Notices to Deliver Remote Access Trojan Across Latin America
The threat actor known as Blind Eagle has resurfaced with a new campaign targeting organizations in Latin America through judicial and administrative-themed phishing lures to deliver a remote access trojan (RAT) that shares its lineage with AsyncRAT and DCRat.
The threat actor known as Blind Eagle has resurfaced with a new campaign targeting organizations in Latin America through judicial and administrative-themed phishing lures to deliver a remote access trojan (RAT) that shares its lineage with AsyncRAT and DCRat.
Assessed to be a Spanish-speaking group and active since 2018, Blind Eagle (aka APT-C-36) has a track record of using spear-phishing lures to distribute commodity RATs like AsyncRAT, BitRAT, Lime RAT, NjRAT, Quasar RAT, and Remcos RAT.
Attack chains begin with phishing emails targeting individuals who handle cases, contracts, judicial, or institutional service requests to trick them into opening a malware-laced attachment.
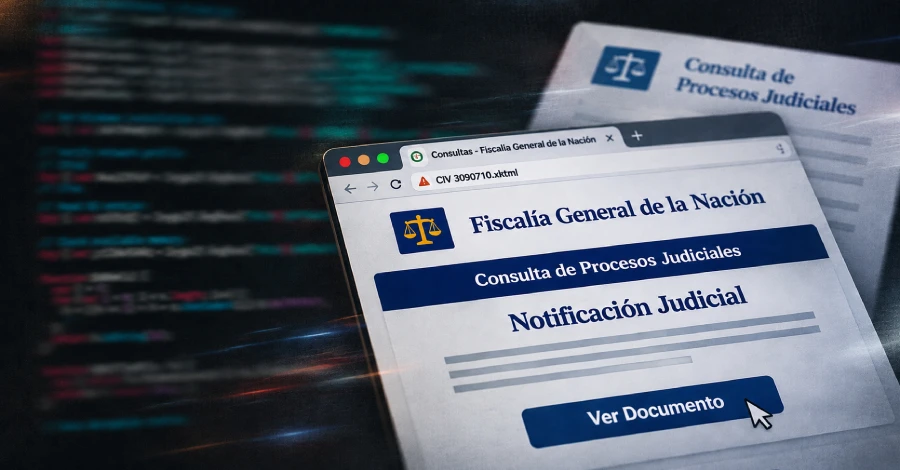
One email containing a Colombian judicial-themed XHTML file has been identified as a weaponized Scalable Vector Graphics (SVG) image that renders a bogus web page impersonating Colombia's Fiscalía General de la Nación, also referred to as the Office of the Attorney General.
The trojan is an AsyncRAT fork with DCRat lineage based on code structure, configuration, build characteristics, and observed behavior.
Present within the ZIP archive is a JavaScript dropper that masquerades as Network Configuration Auditor version 2.7.298.
The JavaScript code conducts environment reconnaissance, and collects details such as system version, network profile, installation date, memory size, computer name, environment variables, and directories localized in Portuguese and Spanish.
Upon execution, it launches a Visual Basic Script that performs Windows Antimalware Scan Interface (AMSI) and Event Tracing for Windows (ETW) bypass, while displaying a fake criminal-citation page as a distraction mechanism.
In parallel, the malware also takes steps to delete the original XHTML artifact, clears Mark of the Web (MotW) metadata, and sets up persistence on the host under the Windows Startup folder so that it's automatically executed on system startup.
These conditions may increase the likelihood of successful compromises and offer greater opportunities to monetize access, steal sensitive data or funds, or reuse compromised credentials against critical systems.
(The story was updated after publication to include further insights from Zenox.)
What happened
The threat actor known as Blind Eagle has resurfaced with a new campaign targeting organizations in Latin America through judicial and administrative-themed phishing lures to deliver a remote access trojan (RAT) that shares its lineage with AsyncRAT and DCRat.
Assessed to be a Spanish-speaking group and active since 2018, Blind Eagle (aka APT-C-36) has a track record of using spear-phishing lures to distribute commodity RATs like AsyncRAT, BitRAT, Lime RAT, NjRAT, Quasar RAT, and Remcos RAT.
Attack chains begin with phishing emails targeting individuals who handle cases, contracts, judicial, or institutional service requests to trick them into opening a malware-laced attachment.
What changed
One email containing a Colombian judicial-themed XHTML file has been identified as a weaponized Scalable Vector Graphics (SVG) image that renders a bogus web page impersonating Colombia's Fiscalía General de la Nación, also referred to as the Office of the Attorney General.
The trojan is an AsyncRAT fork with DCRat lineage based on code structure, configuration, build characteristics, and observed behavior.
Who is affected
Present within the ZIP archive is a JavaScript dropper that masquerades as Network Configuration Auditor version 2.7.298.
The JavaScript code conducts environment reconnaissance, and collects details such as system version, network profile, installation date, memory size, computer name, environment variables, and directories localized in Portuguese and Spanish.
Why it matters
Upon execution, it launches a Visual Basic Script that performs Windows Antimalware Scan Interface (AMSI) and Event Tracing for Windows (ETW) bypass, while displaying a fake criminal-citation page as a distraction mechanism.
In parallel, the malware also takes steps to delete the original XHTML artifact, clears Mark of the Web (MotW) metadata, and sets up persistence on the host under the Windows Startup folder so that it's automatically executed on system startup.
Technical details
These conditions may increase the likelihood of successful compromises and offer greater opportunities to monetize access, steal sensitive data or funds, or reuse compromised credentials against critical systems.
Response
(The story was updated after publication to include further insights from Zenox.)
What to watch next
Watch for additional victim details, indicators of compromise and follow-on exploitation reports.
Watch for revised vendor guidance, fixed versions and mitigation updates.