SGLang RCE Exploit Breaches NEAR AI, Steals Data From 18 Agents and About 100 Users
A remote code execution flaw in SGLang allowed an attacker to breach NEAR AI's servers, compromising data from 18 AI agents and about 100 users.
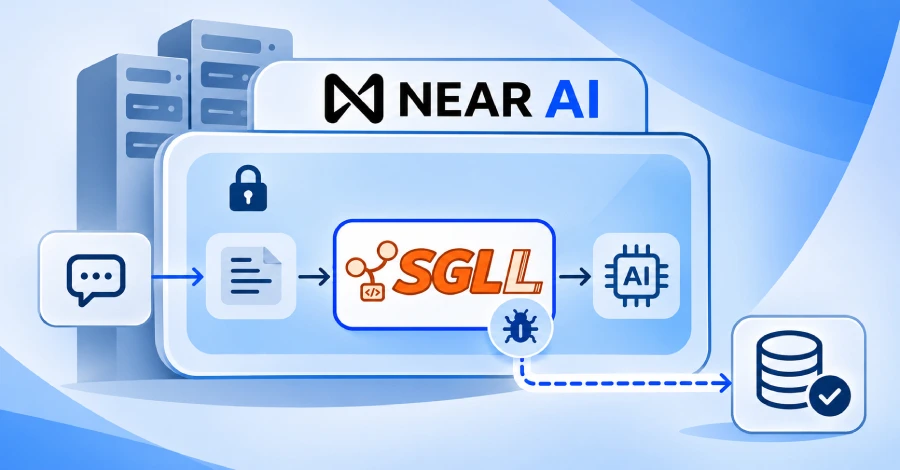
An attacker leveraged a remote code execution vulnerability in SGLang, an open-source inference engine, to infiltrate NEAR AI's systems. This breach occurred last Sunday and led to unauthorized access to sensitive data.
The attacker executed malicious code on one of NEAR AI's inference servers, gaining visibility into requests processed on that server, including those in confidential mode. This mode typically secures requests within a trusted execution environment (TEE) meant to keep them private, even from the company itself. However, NEAR AI acknowledged that the TEE cannot shield against vulnerabilities in the software it runs, which allowed the attacker to access sensitive requests.
Although the company has since closed this access, the attacker managed to penetrate deeper into NEAR AI's infrastructure. They reached an internal system linked to Private Chat, a service NEAR AI had already phased out. Approximately 100 users' account details, including email addresses, names, and some plan and balance information, were compromised. Fortunately, there is no evidence that stored conversations or uploaded files from Private Chat were accessed.
The breach extended to 18 AI agents on an older NEAR AI deployment not housed within the TEE. The attacker extracted data such as chat histories, settings, and logs. Additionally, two customers' NEAR AI Cloud API keys were exposed in logs, prompting the company to revoke them. In response to the incident, NEAR AI revoked all active sessions and administrator credentials, replaced agent tokens, and took Private Chat offline. They also patched the SGLang flaw on all inference servers and completed a forensic review.
NEAR AI has resumed access to its cloud service and reported the flaw to the SGLang project. However, the company has not disclosed the specific SGLang versions affected or whether a fix has been released. They have contacted users whose data was confirmed as accessed and advised all users to be cautious of unexpected messages regarding their accounts or balances. Users not contacted by NEAR AI need not take any action. It remains unclear if any chats handled by NEAR AI's servers for Brave's Leo assistant were involved.
What security teams should do
Revoke and replace compromised API keys and credentials.
Deploy patches for the SGLang vulnerability on all affected servers.
What remains unknown
The specific SGLang versions affected by the flaw are not disclosed.
It is unclear if the SGLang project has released a fix for the vulnerability.
Whether chats for Brave's Leo assistant were processed by the compromised server is not confirmed.