Binance Reveals How Fake Job Interviews and AI Tool Abuse Led to $6.43 Billion Theft
Binance on Tuesday said the record-setting theft of $6.43 billion in assets from the world's largest cryptocurrency exchange was the culmination of a sophisticated, multi-stage campaign that involved the use of a tampered Homebrew installation and recruitment-themed social engineering attack targeting two of its engineers.
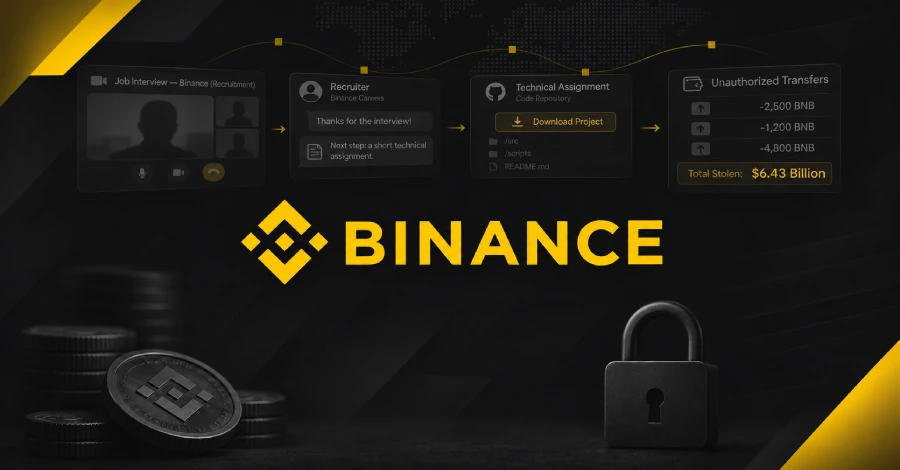
Binance on Tuesday said the record-setting theft of $6.43 billion in assets from the world's largest cryptocurrency exchange was the culmination of a sophisticated, multi-stage campaign that involved the use of a tampered Homebrew installation and recruitment-themed social engineering attack targeting two of its engineers.
The starting point has been traced back to a supply chain attack targeting one of its engineers from the Wallet DevOps team (named Engineer A), who downloaded a trojanized Homebrew installer to install a popular artificial intelligence (AI) tool after searching for it on a search engine.
Although Binance said it detected the attack and rotated all related credentials as a precautionary step, the company said information about The second part of the attack occurred in September 2026, with the threat actor contacting another engineer (named Engineer B) via a legitimate job-hunting platform by disguising themselves as a Project Director.
The attack ultimately exploited its unauthorized access to an internal wallet signing service to initiate transactions outside the normal withdrawal process.
In response to the incident, Binance has reconstructed the affected wallet system in a new environment, as well as rebuilt the internal AI tool and access controls.
Other steps taken as of November 3 are listed below - The entry points identified as having been used in the attack have been closed.
Over the course of the first-round video interview, the HR representative shared a social media account, including personal photos and videos posted on the platform, in an attempt to build credibility and establish trust.
The undetected malware utilized advanced obfuscation and evasion techniques, including substituting a legitimate development tool component with a poisoned version to execute commands and establish communication with an attacker-controlled external server.
Blockchain analysis company Chainalysis has attributed more than $14.3 million in losses over the past 18 months to similar North Korea-linked fake interview schemes, including smaller attacks that helped the attackers hone their tradecraft.
The smaller, successive compromises, which led to losses ranging from tens of thousands to millions, allowed North Korean threat actors to perfect and evolve their methodology, ultimately allowing them to pull off the biggest heist in history , the company added.
Across multiple cases, victims have had their private keys stolen from cloud storage following a bogus interview, indicating that the access extended beyond local files.
Some of the attacks have also been found to employ tactics like EtherHiding to open a resilient command-and-control (C2) channel between victim computers and adversary-controlled infrastructure.
Another approach involves adding redundancy by spreading the C2 communication across two blockchains, TRON and Aptos, to direct infected devices to a third blockchain, BSC, to fetch the malware.
What happened
Binance on Tuesday said the record-setting theft of $6.43 billion in assets from the world's largest cryptocurrency exchange was the culmination of a sophisticated, multi-stage campaign that involved the use of a tampered Homebrew installation and recruitment-themed social engineering attack targeting two of its engineers.
The starting point has been traced back to a supply chain attack targeting one of its engineers from the Wallet DevOps team (named Engineer A), who downloaded a trojanized Homebrew installer to install a popular artificial intelligence (AI) tool after searching for it on a search engine.
Although Binance said it detected the attack and rotated all related credentials as a precautionary step, the company said information about The second part of the attack occurred in September 2026, with the threat actor contacting another engineer (named Engineer B) via a legitimate job-hunting platform by disguising themselves as a Project Director.
What changed
The attack ultimately exploited its unauthorized access to an internal wallet signing service to initiate transactions outside the normal withdrawal process.
In response to the incident, Binance has reconstructed the affected wallet system in a new environment, as well as rebuilt the internal AI tool and access controls.
Other steps taken as of November 3 are listed below - The entry points identified as having been used in the attack have been closed.
Who is affected
Over the course of the first-round video interview, the HR representative shared a social media account, including personal photos and videos posted on the platform, in an attempt to build credibility and establish trust.
The undetected malware utilized advanced obfuscation and evasion techniques, including substituting a legitimate development tool component with a poisoned version to execute commands and establish communication with an attacker-controlled external server.
Why it matters
Blockchain analysis company Chainalysis has attributed more than $14.3 million in losses over the past 18 months to similar North Korea-linked fake interview schemes, including smaller attacks that helped the attackers hone their tradecraft.
The smaller, successive compromises, which led to losses ranging from tens of thousands to millions, allowed North Korean threat actors to perfect and evolve their methodology, ultimately allowing them to pull off the biggest heist in history , the company added.
Technical details
Across multiple cases, victims have had their private keys stolen from cloud storage following a bogus interview, indicating that the access extended beyond local files.
Some of the attacks have also been found to employ tactics like EtherHiding to open a resilient command-and-control (C2) channel between victim computers and adversary-controlled infrastructure.
Response
Another approach involves adding redundancy by spreading the C2 communication across two blockchains, TRON and Aptos, to direct infected devices to a third blockchain, BSC, to fetch the malware.
Attribution
The Hacker News: Binance on Tuesday said the record-setting theft of $6.43 billion in assets from the world's largest cryptocurrency exchange was the culmination of a "sophisticated, multi-stage campaign" that involved the use of a tampered Homebrew installation and recruitment-themed social engineering attack targeting two of its engineers.
What to watch next
Watch for additional victim details, indicators of compromise and follow-on exploitation reports.