Volt Typhoon Used Covert Silent Train Network in Four Zero-Day Exploitation Campaigns
The China-nexus cyber espionage group known as Volt Typhoon has been attributed to a now-disrupted covert access network dubbed Silent Train that has been put to use for zero-day exploitation and strategic access.
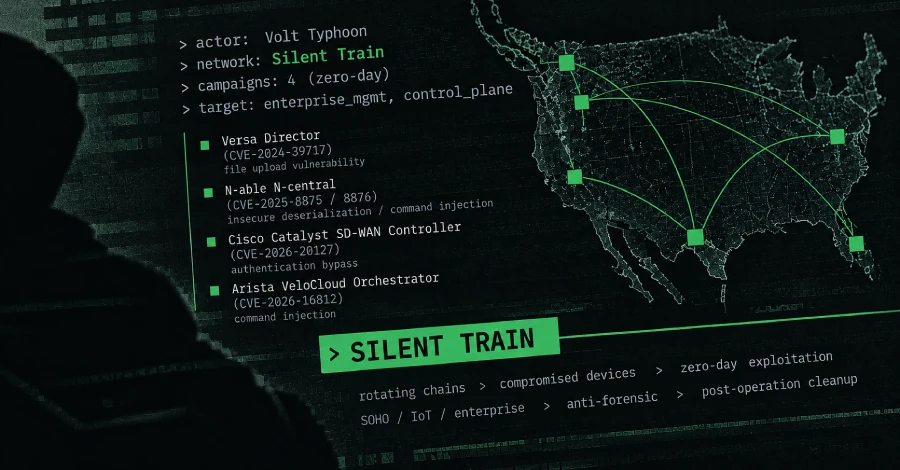
The China-nexus cyber espionage group known as Volt Typhoon has been attributed to a now-disrupted covert access network dubbed Silent Train that has been put to use for zero-day exploitation and strategic access.
The latest findings from Black Lotus Labs show that the security flaw was one among four confirmed zero-day campaigns the threat actor has conducted through Silent Train.
Known to be active since at least 2021, the threat actor was previously observed exploiting a file upload vulnerability in Versa Director as a zero-day (CVE-2024-39717) to deliver a bespoke web shell called VersaMem designed to harvest credentials and enable access to downstream customers.
The remaining three vulnerabilities are listed below - Separately, Volt Typhoon is also suspected to have taken advantage of a likely zero-day vulnerability in Quest KACE before it was patched in October 2025 .
Volt Typhoon (aka Bronze Silhouette, Insidious Taurus, UNC3236, Vanguard Panda, and Voltzite) is the moniker assigned to a China-linked state-sponsored group known for its targeting of critical infrastructure networks, particularly communications, energy, transportation, and water and wastewater systems sectors.
The campaign is estimated to have impacted more than 30 victims.
What's interesting is that the covert access capability began to take shape sometime around November 2023, just weeks before the first round of disruption targeting KV-botnet , an IoT botnet linked to multiple China-nexus state-sponsored threat actors, including Volt Typhoon.
Through repeated targeting of centralized management platforms and control plane technologies, Silent Train shows how Volt Typhoon systematically pursues and preserves access to some of the most consequential networks in the United States."
Each link in the chain serves a specific purpose - No less than 27 device classes, ranging from SOHO and IoT devices (e.g., TP-Link, Intelbras, Ruckus Wireless, SATO, NETGEAR, Zyxel, and Cambium) to enterprise platforms (e.g., Fortinet, Cisco, PRTG, Mirth Connect, and CyberPanel), have been exploited and enrolled into the covert network.
Subsequent maturation of the platform introduced reverse-tunnel variants that used open-source proxies like Chisel and FRP to send traffic from infected devices to upstream infrastructure.
What happened
The China-nexus cyber espionage group known as Volt Typhoon has been attributed to a now-disrupted covert access network dubbed Silent Train that has been put to use for zero-day exploitation and strategic access.
The latest findings from Black Lotus Labs show that the security flaw was one among four confirmed zero-day campaigns the threat actor has conducted through Silent Train.
What changed
Known to be active since at least 2021, the threat actor was previously observed exploiting a file upload vulnerability in Versa Director as a zero-day (CVE-2024-39717) to deliver a bespoke web shell called VersaMem designed to harvest credentials and enable access to downstream customers.
The remaining three vulnerabilities are listed below - Separately, Volt Typhoon is also suspected to have taken advantage of a likely zero-day vulnerability in Quest KACE before it was patched in October 2025 .
Who is affected
Volt Typhoon (aka Bronze Silhouette, Insidious Taurus, UNC3236, Vanguard Panda, and Voltzite) is the moniker assigned to a China-linked state-sponsored group known for its targeting of critical infrastructure networks, particularly communications, energy, transportation, and water and wastewater systems sectors.
The campaign is estimated to have impacted more than 30 victims.
Why it matters
What's interesting is that the covert access capability began to take shape sometime around November 2023, just weeks before the first round of disruption targeting KV-botnet , an IoT botnet linked to multiple China-nexus state-sponsored threat actors, including Volt Typhoon.
Through repeated targeting of centralized management platforms and control plane technologies, Silent Train shows how Volt Typhoon systematically pursues and preserves access to some of the most consequential networks in the United States."
Technical details
Each link in the chain serves a specific purpose - No less than 27 device classes, ranging from SOHO and IoT devices (e.g., TP-Link, Intelbras, Ruckus Wireless, SATO, NETGEAR, Zyxel, and Cambium) to enterprise platforms (e.g., Fortinet, Cisco, PRTG, Mirth Connect, and CyberPanel), have been exploited and enrolled into the covert network.
Response
Subsequent maturation of the platform introduced reverse-tunnel variants that used open-source proxies like Chisel and FRP to send traffic from infected devices to upstream infrastructure.
Attribution
The Hacker News: The China-nexus cyber espionage group known as Volt Typhoon has been attributed to a now-disrupted covert access network dubbed Silent Train that has been put to use for zero-day exploitation and strategic access.
What to watch next
Watch for new exploitation reports and updated indicators of compromise.
Watch for updated vendor guidance and fixed-version details.