Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link
Details have emerged about a high-severity security flaw in the Elementor Website Builder WordPress plugin that could be exploited by an unauthenticated attacker to create rogue administrator accounts and take control of a site.
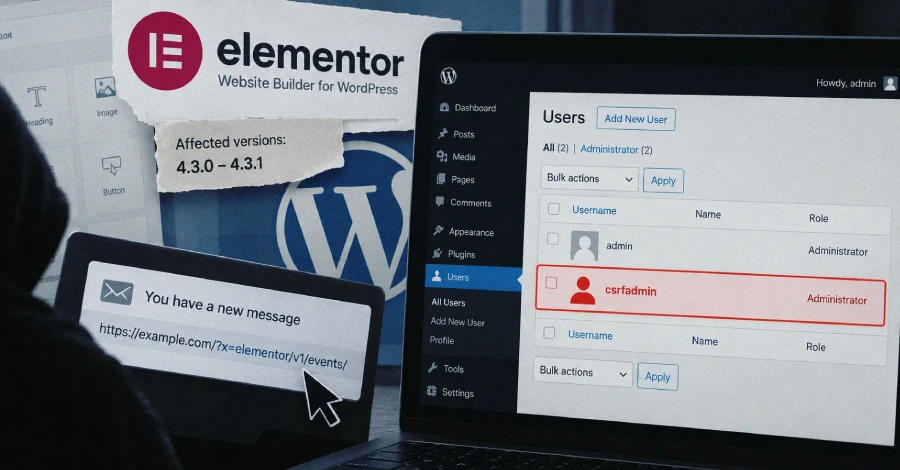
Details have emerged about a high-severity security flaw in the Elementor Website Builder WordPress plugin that could be exploited by an unauthenticated attacker to create rogue administrator accounts and take control of a site.
According to Patchstack’s analysis, the CSRF flaw is caused by Elementor’s Editor Events module checking the raw request URI for the elementor/v1/events/ path and bypassing WordPress’s REST nonce validation when that string is present.
Patchstack says the flaw can be abused in one-click attacks against a logged-in administrator to create a new attacker-controlled admin account.
It only affects versions 4.3.0 and 4.3.1 of the plugin, which is active on over 10 million WordPress sites.
An attacker could exploit this loophole to create an administrator account through "/wp/v2/users" using a request like below - Because Elementor releases before 4.3.0 do not ship the Editor Events proxy, they are not affected by the flaw.
A cross-site request forgery (CSRF) vulnerability in the Elementor plugin for WordPress could allow an unauthenticated attacker to create administrator accounts.
Threat actors can exploit the flaw by tricking a logged-in administrator into opening a malicious link, causing the victim's authenticated session to perform a REST API action permitted by their account.
WordPress backup plugin flaw exposes millions of sites to takeover attacks
Statistics from WordPress.org show that the two impacted versions alone have been installed on more than 2 million sites.
The CSRF flaw has yet to receive an identifier and impacts only versions 4.3.0 and 4.3.1.
What happened
Details have emerged about a high-severity security flaw in the Elementor Website Builder WordPress plugin that could be exploited by an unauthenticated attacker to create rogue administrator accounts and take control of a site.
According to Patchstack’s analysis, the CSRF flaw is caused by Elementor’s Editor Events module checking the raw request URI for the elementor/v1/events/ path and bypassing WordPress’s REST nonce validation when that string is present.
What changed
Patchstack says the flaw can be abused in one-click attacks against a logged-in administrator to create a new attacker-controlled admin account.
It only affects versions 4.3.0 and 4.3.1 of the plugin, which is active on over 10 million WordPress sites.
Who is affected
An attacker could exploit this loophole to create an administrator account through "/wp/v2/users" using a request like below - Because Elementor releases before 4.3.0 do not ship the Editor Events proxy, they are not affected by the flaw.
A cross-site request forgery (CSRF) vulnerability in the Elementor plugin for WordPress could allow an unauthenticated attacker to create administrator accounts.
Why it matters
Threat actors can exploit the flaw by tricking a logged-in administrator into opening a malicious link, causing the victim's authenticated session to perform a REST API action permitted by their account.
WordPress backup plugin flaw exposes millions of sites to takeover attacks
Technical details
Statistics from WordPress.org show that the two impacted versions alone have been installed on more than 2 million sites.
The CSRF flaw has yet to receive an identifier and impacts only versions 4.3.0 and 4.3.1.
The cross-site request forgery (CSRF) vulnerability, which has yet to be assigned a CVE identifier, carries a CVSS score of 8.8 out of 10.0.
Response
Users of the plugin are advised to apply the latest update as soon as possible to counter any potential threat.
Following responsible disclosure, the issue has been addressed in version 4.3.2 released earlier this week.
What security teams should do
Security firm Patchstack reported the vulnerability to the Elementor team on September 22 after receiving it from bug hunter “Saggre.” Elementor released a fix two days later, in version 4.3.2 of the plugin.
Users of the plugin are recommended to upgrade to Elementor version 4.3.2 as soon as possible, which prevents attackers from triggering the bypass through the query string.
Attribution
The Hacker News: Details have emerged about a high-severity security flaw in the Elementor Website Builder WordPress plugin that could be exploited by an unauthenticated attacker to create rogue administrator accounts and take control of a site.
BleepingComputer: A cross-site request forgery (CSRF) vulnerability in the Elementor plugin for WordPress could allow an unauthenticated attacker to create administrator accounts.
What to watch next
Watch for new exploitation reports and updated indicators of compromise.
Watch for updated vendor guidance and fixed-version details.