Race to update services' computer systems after cyber-security flaw found
Organisations and businesses are still scrambling to update their systems after cyber-security flaws were revealed in a widely-used programming language, PHP.
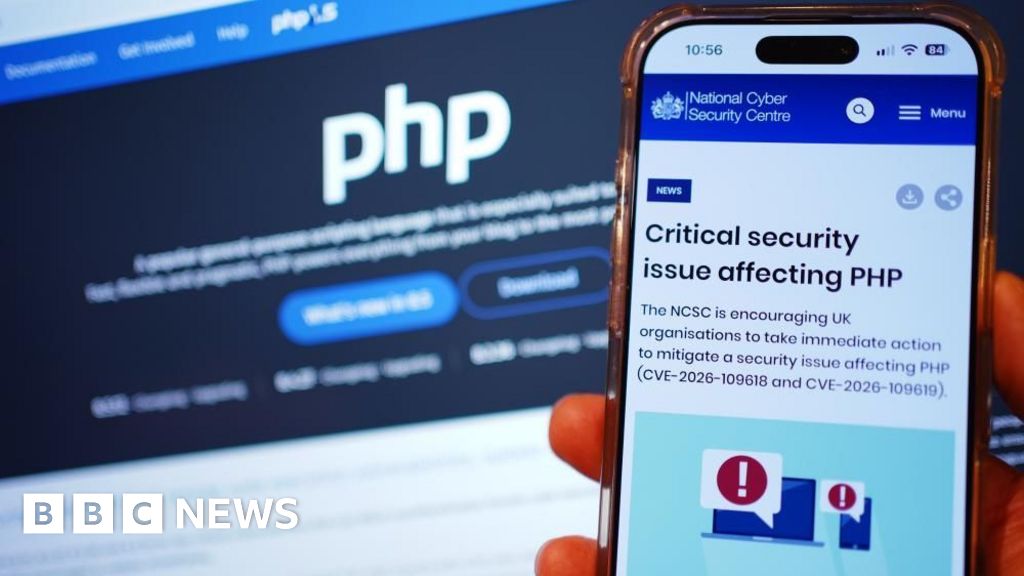
Organisations and businesses are still scrambling to update their systems after cyber-security flaws were revealed in a widely-used programming language, PHP.
Matthew Prince, the boss of internet infrastructure firm Cloudflare, wrote on X on Thursday that the company saw "thousands" of attempts to exploit the PHP vulnerabilities across its network in the 10 hours before it was publicly announced.
Websites around the world were taken offline on Wednesday and Thursday after the developers of PHP said "critical vulnerabilities" were found in the back-end language, used in web development for decades.
Researchers warned the "severe" flaws could expose millions of sites using it to potential hacks if left unpatched - and the UK government was among those to take some sites offline as a precaution.
In the attack, an anonymous internet address attempted to target weaknesses in one of Amazon's decoy or "honeypot" systems, the company's security chief CJ Moses said.
The US National Security Agency told all organisations that use PHP to take their systems offline if they were unable to patch them immediately, adding that the flaw could provide a "direct path" to exploit a system's database.
While the impact of the PHP flaw remains to be seen, disruption continued for businesses and organisations after many sites were taken down on Wednesday.
The UK government says it is working to identify any potential exposure in its online services, after critical cyber-security flaws were identified in the PHP programming language that underpins a significant number of the world's websites.
Governments and some of the world's biggest companies are rushing to protect systems that use PHP before hackers can exploit the flaws.
It added there were further "exploitation attempts" once the embargo on the flaw warning was lifted.
What happened
Organisations and businesses are still scrambling to update their systems after cyber-security flaws were revealed in a widely-used programming language, PHP.
Matthew Prince, the boss of internet infrastructure firm Cloudflare, wrote on X on Thursday that the company saw "thousands" of attempts to exploit the PHP vulnerabilities across its network in the 10 hours before it was publicly announced.
What changed
Websites around the world were taken offline on Wednesday and Thursday after the developers of PHP said "critical vulnerabilities" were found in the back-end language, used in web development for decades.
Researchers warned the "severe" flaws could expose millions of sites using it to potential hacks if left unpatched - and the UK government was among those to take some sites offline as a precaution.
Who is affected
In the attack, an anonymous internet address attempted to target weaknesses in one of Amazon's decoy or "honeypot" systems, the company's security chief CJ Moses said.
The US National Security Agency told all organisations that use PHP to take their systems offline if they were unable to patch them immediately, adding that the flaw could provide a "direct path" to exploit a system's database.
Why it matters
While the impact of the PHP flaw remains to be seen, disruption continued for businesses and organisations after many sites were taken down on Wednesday.
The UK government says it is working to identify any potential exposure in its online services, after critical cyber-security flaws were identified in the PHP programming language that underpins a significant number of the world's websites.
Technical details
Governments and some of the world's biggest companies are rushing to protect systems that use PHP before hackers can exploit the flaws.
It added there were further "exploitation attempts" once the embargo on the flaw warning was lifted.
These vulnerabilities are flaws in PHP itself, not in the hosted application or its configuration," the NSA said in a later update.
Response
While the PHP Foundation intended to release its discovery later this month along with a complete fix for the problem, usually referred to by software developers as a "patch", details of the flaw were leaked on social media on Tuesday.
A spokesperson said work had already taken place across government to "identify and fix potential exposures to our systems and our experts are continuing to work closely with both OpenAI and international partners on this issue".
What security teams should do
The company said it "automatically detected and restricted malicious scanning attempts targeting this vulnerability." PHP powers a vast number of platforms, including online shops, Wikipedia and WordPress – the content management system behind many websites like blogs.
But Austin said this incident is not necessarily bad news because organisations would now "run and patch PHP immediately" if they haven't already.
Attribution
BBC News: Organisations and businesses are still scrambling to update their systems after cyber-security flaws were revealed in a widely-used programming language, PHP.
BBC News: The UK government says it is working to identify any potential exposure in its online services, after critical cyber-security flaws were identified in the PHP programming language that underpins a significant number of the world's websites.
BBC News: For more than a decade, serious flaws had gone undetected in the technology underpinning much of the internet.
What to watch next
Watch for new exploitation reports and updated indicators of compromise.
Watch for updated vendor guidance and fixed-version details.